
This article reviews five software development firms for building secure, AI-driven payment processing modules: Softjourn, ScienceSoft, PowerGate Software, Andersen, and EPAM Systems. The comparison examines each firm’s publicly documented security measures, the use of AI in payment operations, and its experience in developing payment products.
1. How we assessed each firm
We compared the five firms based on three criteria:
- Security: Publicly documented ISO/IEC 27001 certifications, PCI DSS credentials, and payment-related security measures. Company certifications are distinguished from platform- or client-specific credentials.
- AI in payment operations: Evidence of AI or machine learning for fraud detection and transaction monitoring. Rules-based controls are distinguished from machine-learning applications, and vendor-described capabilities from named client deployments. General AI services and AI-assisted software development are excluded.
- Payment module projects: Published client projects involving payment gateways, card platforms, money transfers, transaction processing, and other payment infrastructure.
2. What are the best software development firms for building secure, AI-driven payment processing modules?
|
Company |
Security |
AI in payment operations |
Payment module projects |
|---|---|---|---|
|
Softjourn |
PCI DSS-compliant payment technology; no public ISO 27001 certificate details |
Rules-based fraud control for iKobo; operated separately from the core platform |
iKobo money transfers; UPC TPII card processing |
|
ScienceSoft |
ISO/IEC 27001:2022; PCI DSS compliance services |
AI-based payment-fraud prevention; no named client deployment identified. |
White-label e-commerce payment gateway with 3-D Secure |
|
PowerGate Software |
ISO 27001:2022; PCI DSS Level 1 reported for gateway platform |
No payment-specific AI implementation identified in published projects |
White-label payment gateway; multi-currency card platform |
|
Andersen |
PCI DSS AOC for assessed services |
LSTM-based transaction anomaly detection implemented in a FinTech platform |
DECTA payment and card issuance; UK bank clearing-platform modernization |
|
EPAM Systems |
PCI DSS certification listed in ImageNPay case study; scope unspecified |
No named AI/ML implementation identified in the payment projects reviewed |
National instant-payment network; POS processing; retail payment hub |
Note: The information in this article was last reviewed on November 13, 2026, using information published on the providers’ official websites and B2B service listing platforms. The order of companies in the comparison does not indicate a ranking or endorsement.
2.1 Softjourn
Softjourn works in fintech and payment technology, with published experience in money transfers, card processing, and payment security.
Security: Payment security capabilities include PCI DSS-compliant technology for processing, transmitting, and storing card data, as well as EMV, 3-D Secure (3DS), end-to-end encryption, hardware security modules (HSMs), and tokenization. Public materials reviewed do not provide ISO 27001 certificate details or certification scope. A separate PEX project involved Azure security controls, SIEM capabilities, and PCI-related security activities. These demonstrate project-level security work, not company-wide PCI DSS certification.
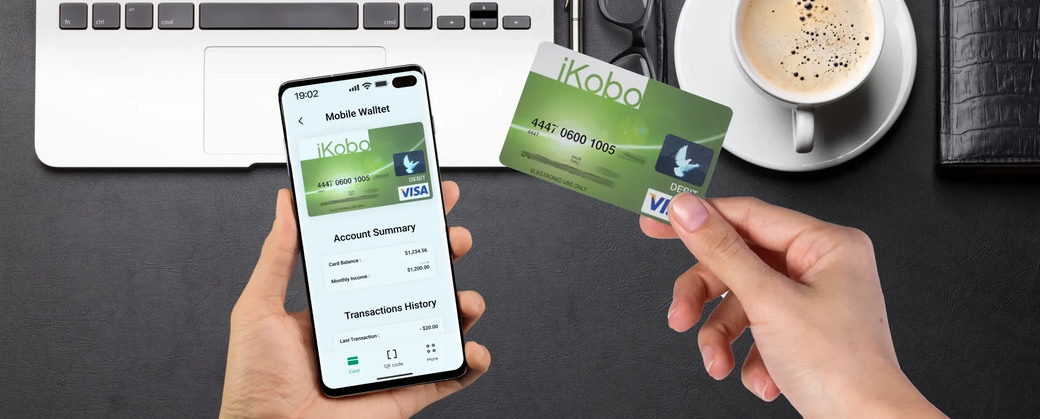
AI in payment operations: The iKobo project included a rules-based fraud-control system that checked transactions and could block accounts while the client’s staff investigated suspicious activity. The system operated separately from the core platform, on its own machine and database. The case study describes this as rules-based AI but does not identify machine learning or predictive risk scoring.
Payment module projects:
- iKobo: Included peer-to-peer money transfers and improvements to merchant processing. The project also helped streamline settlements with U.S. banks.
- UPC: Maintenance and enhancements covered UPC’s Unix-based TPII card-processing system, which handles transaction authorization across issuers, acquirers, ATMs, and POS terminals. UPC’s PCI DSS compliance should be distinguished from Softjourn’s role as its technology partner.
Best fit if: You need a development partner with experience in money transfers, card-processing infrastructure, payment security, and rules-based fraud controls, particularly for platforms that need a separate fraud-screening component.
Website: https://softjourn.com/
Source: softjourn
2.2 ScienceSoft
Custom payment gateways and 3-D Secure authentication are the clearest parts of ScienceSoft’s published payment portfolio.
Security:
- ISO/IEC 27001:2022: Certification covers the information security management system for software design, development, and technical support.
- PCI DSS: Services include compliance gap assessments, security policy improvements, testing, and implementation of controls to protect cardholder data. These are consulting and implementation services, not evidence of PCI DSS certification held by ScienceSoft itself.
AI in payment operations: AI-based fraud prevention, including real-time detection of suspicious transaction patterns, anomaly detection, and payer behavior analysis. No named client deployment of these capabilities is publicly documented.
Payment module projects: In a case for a European fintech product company, ScienceSoft developed a white-label e-commerce payment gateway with 3-D Secure. The implementation included:
- Backend integration: 3DS components and APIs connecting the gateway with core banking systems, HSMs, card cryptography generation systems, fraud detection tools, and e-merchant applications.
- EMVCo 3DS: Support for versions 1.0.2, 2.1.0, and 2.2.0.
- Access Control Server (ACS): Evaluated transaction risk based on payer history, transaction value, and device and browser information to determine whether additional cardholder authentication was required. This is risk-based authentication; the case study does not identify it as an AI feature.
- PA-DSS: The project referenced requirements applicable at the time. PA-DSS was retired on 28 October 2022, so this historical reference does not establish current PCI Secure Software validation.
Best fit if: You need custom payment gateway development, 3-D Secure components, or PCI DSS compliance support. For AI-based fraud prevention, request additional client references to verify production experience.
Website: https://www.scnsoft.com/
2.3 PowerGate Software
Published payment projects cover two product areas: A cloud-native white-label gateway and a multi-currency card platform. Both demonstrate experience developing payment products for financial services.
Security:
- ISO 27001:2022: Published security practices include structured risk management, access controls, isolated environments, traceable change logs, and business continuity measures such as data backups and disaster recovery planning.
- PCI DSS Level 1: A payment gateway case study in 2019 reports this certification for the platform. This is a platform-level credential, not a PCI DSS certification held by PowerGate Software itself.
AI in payment operations: No payment-specific AI implementation has been identified in the published gateway or card-platform projects. The available case studies demonstrate payment product development experience, but do not document AI-based fraud detection, transaction monitoring, or automated payment decisions.
Payment module projects:
- White-label payment gateway: Development of a cloud-native payment gateway for financial institutions and merchants, supporting digital payments and e-commerce acquiring. The case study identifies Swedbank, SEB, and LHV as users and reports more than 500,000 transactions processed annually.
- Multi-currency card platform: In 2019, PowerGate worked with a UK-based partner to develop a card platform supporting currency exchange and Mastercard debit-card use. Features included real-time spending tracking, balance alerts, online bank account management, card controls, and the ability to block lost or stolen cards.
Best fit if: You need a development partner for white-label payment gateways, multi-currency card products, or secure payment infrastructure. Its published projects demonstrate payment product engineering, but do not document AI functionality within payment workflows.
Website: https://powergatesoftware.com/
A team meeting at PowerGate Software’s office, discussing a project using a shared presentation and laptops.
2.4 Andersen
Andersen’s financial services portfolio covers payment platforms, card issuance, payment clearing, and transaction anomaly detection. Its PCI DSS Attestation of Compliance (AOC) provides additional security evidence relevant to payment software projects.
Security: The PCI DSS AOC covers systems security services, payment software development, IT support, application and infrastructure support and maintenance, and merchant services.
AI in payment operations: In a project for a Baltic FinTech company and EU-licensed eMoney institution, Andersen developed a financial platform covering payment gateway functionality, international transfers, and payment card services. One feature uses an LSTM neural network trained on transaction logs to identify deviations from normal customer behavior and help detect potentially suspicious financial activity. The case study does not specify whether the model participates in payment authorization or automatically blocks transactions.
Payment module projects:
- DECTA: Development of an online payment and card issuance platform for a Latvia-based fintech company. Features include payment and order management, invoice management, virtual card issuance, payment initiation, subscriptions, recurring payments, and MOTO transactions.
- UK clearing bank: Modernization of an existing payment clearing platform for a British clearing bank. The work focused on redesigning development portals, updating dependencies, improving documentation, and addressing security issues. This was modernization work, not development of the entire clearing system from scratch.
Best fit if: You need payment platform development, card issuance, or banking payment infrastructure modernization, with a documented example of LSTM-based transaction anomaly detection in a FinTech platform.
Website: https://andersenlab.com/
An Andersen presenter delivers a technical presentation on Appium locators at a company event.
2.5 EPAM Systems
EPAM’s Open Banking & Payments practice covers payment infrastructure, processing platforms, and digital payment hubs. Published projects include national instant-payment networks, POS processing, and retail payment hubs.
Security: PCI DSS certification is mentioned in EPAM’s ImageNPay case study (a prepaid virtual Mastercard application). However, the case study does not identify the certificate holder or assessment scope, so this reference does not establish company-wide PCI DSS certification for EPAM.
AI in payment operations: The published payment projects reviewed do not identify a named client deployment of AI for fraud detection, transaction monitoring, or payment authorization. EPAM’s case studies demonstrate experience in payment infrastructure and processing, but do not establish AI functionality operating within the payment workflows discussed.
Payment module projects:
- National instant-payment network: Design of an instant-payment solution for a European country. The solution became the official national platform, with banks required to connect to it.
- Payment service provider: Development of a microservices-based payment-processing capability for a leading POS machine provider, adding alternative payment methods, QR code payments, and other payment options.
- Retail digital payments hub: Development of a payment hub for a global sports apparel manufacturer, featuring payment switching and integrations with payment service providers and fraud solutions.
Best fit if: You need an engineering partner for payment infrastructure, POS processing, or digital payment hubs.
Website: https://www.epam.com/
3. Frequently asked questions
3.1 Does PCI DSS compliance in a project mean the software development company is PCI DSS-compliant?
Not necessarily. PCI DSS evidence may apply to a client’s environment, a specific payment platform, or a service provider. Check the AOC or other relevant compliance evidence to identify the assessed entity, services, and systems. A client’s or platform’s compliance status does not automatically extend to the software developer.
3.2 Does AI in payment processing always mean machine learning?
No. Payment-related AI can include rules-based fraud controls, machine-learning anomaly detection, or other automated analysis. These approaches work differently, so ask the vendor which technology was used and what role it played in the payment system.
3.3 Does AI need to make the final decision on every transaction?
No. Staff can retain responsibility for final transaction decisions. AI can identify suspicious patterns and provide risk scores or alerts for staff to review. Predefined controls may still trigger automated actions, such as blocking an account while staff investigates, as demonstrated in Softjourn’s iKobo project. The system requirements should clearly define which actions can be automated and which require staff approval.
3.4 How should you evaluate transaction figures in a company’s case study?
Check the publication date, reporting period, and what the figures measure, such as annual transaction volume or total processed value. Historical company-reported figures should not be treated as independently verified current performance.
3.5 What should be defined before developing an AI-driven payment module?
Before development, define the payment functions the module needs to support, including transaction authorization, payment routing, fraud detection, and reconciliation. Specify how AI will help staff identify and review suspicious transactions, as well as the security requirements for the payment data and systems involved. Also, set requirements for transaction latency, processing capacity, availability, and fraud detection accuracy.
Among the five software development firms for building secure, AI-driven payment processing modules, published evidence of AI in payment operations varies. Softjourn documents a rules-based fraud-control system in iKobo, while Andersen reports LSTM-based transaction anomaly detection in a FinTech platform. ScienceSoft’s published materials cover AI-based fraud-prevention capabilities, but do not identify a named client deployment. EPAM’s reviewed payment projects do not document a named AI/ML implementation. PowerGate’s evidence is stronger for payment product engineering than for AI functionality within payment workflows.